
Sad news from the high-stakes cash game community: over ten (and possibly even more) regulars were scammed out of several million dollars across GG, ACR, and Coin.
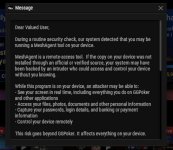
A cheater—or more likely, a group of cheaters—somehow managed to install spyware on the computers of numerous regulars, gaining access to their screens. The scammer was clever enough to avoid immediate detection and spent months targeting specific regulars who had installed the Trojan.
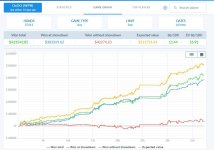
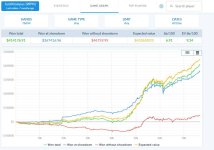
In the end, he was finally unmasked—after all, greed occasionally caused him to slip up. Furthermore, his results were so exceptional that people began investigating; they discovered a pattern showing that he had won all his money from specific regulars and played over 90% of his hands against them—meaning he was deliberately table-selecting them—and eventually, the Trojan itself was discovered. The Trojan was almost certainly distributed via some form of poker software—likely through multiple channels, such as a tracker or a table-arrangement tool—and also pushed via phishing emails; basically, they were attacking on all fronts.
It seems to have been installed via "Intuitive Tables" , though it could have been other programs (possibly even through collusion with the developers).
The Trojan itself is named "Mesh Agent" (you can check your system for the process or traces of it).
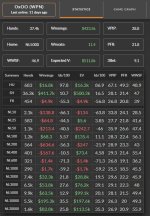
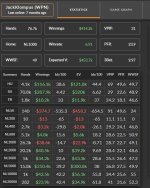
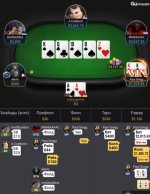
Screenshots show the cheater's main screen names on ACR, their real identity on GG (along with the hand that gave them away), and more.